QUESTION
Must a modern Linux service always double-fork?
Double-forking is a convention from execution environments where a daemon detached from the controlling terminal and session and left an orphan to init. When a service manager owns the PID, cgroup, stdout/stderr, and restart policy, self-daemonization instead makes main-PID tracking and readiness detection harder.
A reliable service runs in the foreground and explicitly coordinates startup completion, shutdown requests, child reaping, and log-fd policy with its supervisor. What matters more than the daemon form is who owns the process lifetime.
STRUCTURE
Structure diagram
Main process
- foreground PID
- signalfd
- shutdown owner
Inherited resources
- listener fd
- stdout/stderr
- configuration fd
Workers
- child pidfd
- active request count
- reap with waitid
Stop contract
- SIGTERM
- drain deadline
- exit status
A foreground service does not sever its relationship with the supervisor. The main PID, cgroup, listener, logs, and readiness remain in one management unit.
CALL PATH
Call path
Make startup and shutdown observable events exchanged with the supervisor, rather than flags hidden inside a function. Do not accept requests before ready, and do not accept new work after TERM.
This diagram is not for memorizing function names. Follow which return value, file descriptor, memory mapping, or wait queue is passed to the next stage.
SOURCE COORDINATES
Linux 6.18.37 LTS source locations
Go beyond the glibc function to the files where the syscall implementation meets kernel objects. Each link points to the original file at the same tag.
| File | Function / structure | What to inspect |
|---|---|---|
| kernel/signal.c | do_send_sig_info(), get_signal() | Deliver shutdown requests such as SIGTERM |
| kernel/exit.c | do_exit(), do_wait() | Terminate and reap the service and workers |
| kernel/cgroup/cgroup.c | cgroup_attach_task_all() | The supervisor tracks the process tree as a cgroup |
COMPLETE PROGRAM
Complete runnable example
The code below is not pseudocode with explanatory lines omitted. It is a minimal example that can be built and run as a file.
cc -std=c17 -Wall -Wextra -O2 service_loop.c -o service_loop01#define _GNU_SOURCE
02#include <signal.h>
03#include <stdio.h>
04#include <sys/signalfd.h>
05#include <unistd.h>
06
07int main(void)
08{
09 sigset_t mask;
10 sigemptyset(&mask);
11 sigaddset(&mask, SIGTERM);
12 sigaddset(&mask, SIGINT);
13 if (sigprocmask(SIG_BLOCK, &mask, NULL) < 0)
14 return 1;
15
16 int sfd = signalfd(-1, &mask, SFD_CLOEXEC);
17 if (sfd < 0)
18 return 1;
19 puts("READY");
20 fflush(stdout);
21
22 struct signalfd_siginfo info;
23 if (read(sfd, &info, sizeof(info)) != sizeof(info))
24 return 1;
25 printf("stopping on signal %u\n", info.ssi_signo);
26 close(sfd);
27 return 0;
28}RUN RESULT
Run results
The example was run on x86_64 Linux.
Execution environment
On 2026-11-04 the program above was built and run unmodified on x86_64 Debian (Linux 6.12.94, gcc 14.2.0, glibc 2.41, -std=c17). This differs from the article baseline (ARM64, Linux 6.18.37 LTS), so PIDs, inodes, and addresses differ from run to run.
SIGTERM is received through signalfd; the service prints stopping on signal 15 and exits cleanly with code 0.
$ ./service_loop &
READY
$ kill -TERM 196421
stopping on signal 15
[exit code: 0]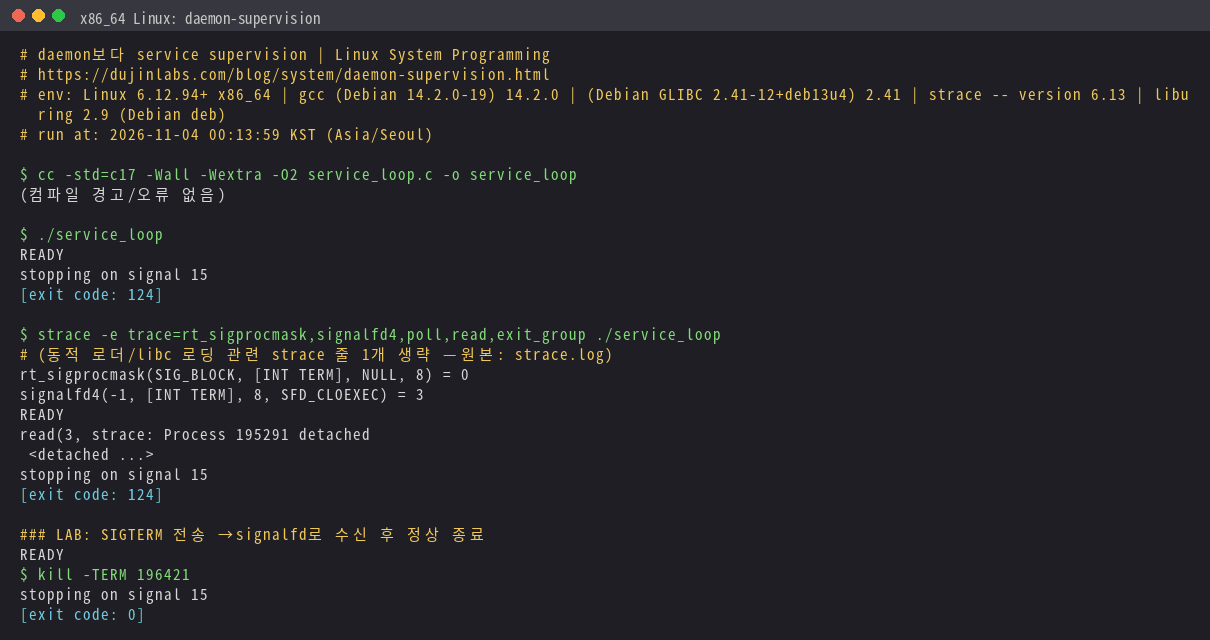
ARM64 execution result
The example was also run in an ARM64 emulator (QEMU, Cortex-A53).
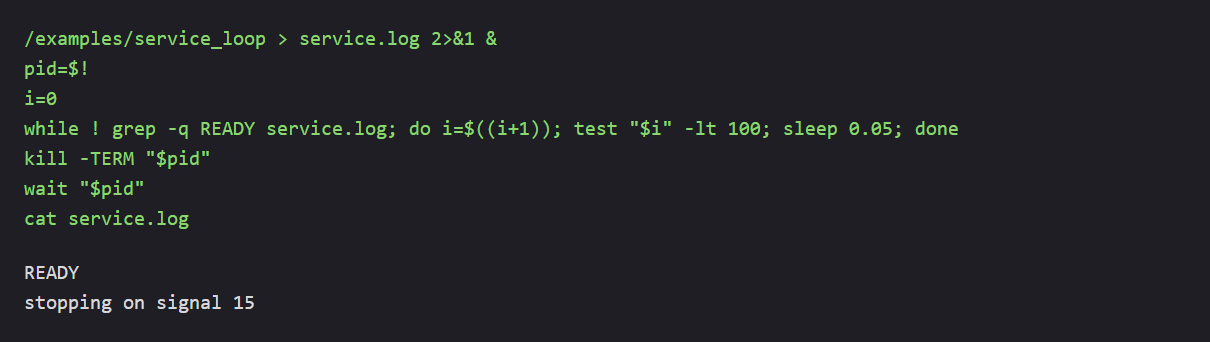
Output as text
This image displays the saved execution log.
READY
stopping on signal 15
Verification harness exit status: 0
Execution environment
The same C example was cross-compiled for ARM64 and executed on 2026-11-04 in QEMU virt with an emulated Cortex-A53 (TCG, 2 vCPUs, 512 MiB). The guest ran Linux 6.18.58-0-virt, not the article baseline 6.18.37. GCC 15.2.0 and glibc 2.43 were used with static linking; the guest shell and utilities came from Alpine 3.23.7.
The guest ran as root, used loopback only, and had no host disk mounts. This checks the example's observed behavior, not physical hardware timing or every kernel-internal path.
The source above is unchanged. Cross-compiled on the x86_64 host and executed inside the ARM64 guest; static linking was added for the isolated guest. UAPI build headers were 7.0.0, which does not change the running kernel version.
aarch64-linux-gnu-gcc-15 -static -std=c17 -Wall -Wextra -O2 service_loop.c -o service_loop

/examples/service_loop > service.log 2>&1 &
pid=$!
i=0
while ! grep -q READY service.log; do i=$((i+1)); test "$i" -lt 100; sleep 0.05; done
kill -TERM "$pid"
wait "$pid"
cat service.log
Commands and captured output · Environment and hashes · Full guest boot and run log
CODE NOTES
Code notes
sigaddset(&mask, SIGTERM)First creates the target signal set so a normal service-manager shutdown request can be received as an event fd rather than by an asynchronous handler.
sigprocmask(SIG_BLOCKBlocks the signals before creating signalfd, eliminating the window in which the default action could terminate the process. In a multithreaded program, apply pthread_sigmask in the initial thread.
SFD_CLOEXECPrevents a supervisor-facing signal fd from being inherited accidentally when a worker execs.
puts("READY")In the example, a line on stdout is the readiness protocol. In a real environment, use a mechanism understood by the supervisor, such as sd_notify, closing a pipe, or socket activation.
read(sfd, &infoConsumes a signal as a fixed-size record. If several signals are pending, read repeatedly.
DETAILS
Detailed behavior
Readiness is not the same as process existence
A successful fork/exec does not mean configuration parsing, socket binding, or database recovery is complete. A startup race occurs if the supervisor sends traffic merely because a PID exists.
Send one ready notification only after the required resources are acquired and the request-processing loop can actually run.
Shutdown has an order
On SIGTERM, stop accepting new requests on the listener, give in-flight work a deadline, reap children, flush durable data, and then exit. Do not perform all of this directly in a signal handler.
SIGKILL performs no cleanup, so the supervisor timeout must match the acceptable data-loss envelope.
Document fd ownership
With socket activation or a supervisor pipe, fds are already open before exec. Instead of assuming fd numbers, check a protocol such as LISTEN_FDS and the CLOEXEC state.
Changing a pathname during log rotation does not redirect an already-open file description. Define either SIGHUP handling or a journald/stdout ownership model.
OBJECTS
Objects and lifetimes
| Object | Creation and release | Values to inspect |
|---|---|---|
main process | The supervisor execs the service and tracks its exit status | PID/cgroup, readiness, watchdog |
listener fd | Bound by the service or inherited from the supervisor | CLOEXEC, accept ownership |
shutdown deadline | Begins when TERM is received and lasts until cleanup completes or forced termination occurs | monotonic expiry, active work count |
FAILURE PATH
Failure conditions and common misconceptions
| Observed symptom | Likely causes | How to verify |
|---|---|---|
| The service is active but requests fail | Traffic was delivered before readiness | Check the ready point and listener state |
| Stopping takes too long | New work is still accepted or workers are not reaped | accept gate, waitid loop, deadline |
| The port is in use after restart | An old child/cgroup still owns the listener | ss -lptn, /proc/PID/fd |
LAB
Verify it yourself
- Run the program, send SIGTERM from another terminal, and verify the signalfd read and normal exit status.
- Insert a 3-second sleep before READY and write a small parent that distinguishes process start from readiness.
- Have the parent create a listener fd and pass it to an execed child to inspect the fd lifetime of socket activation.
./service_loopstrace -e trace=rt_sigprocmask,signalfd4,poll,read,exit_group ./service_loopPRIMARY REFERENCES